
Imagine being a CISO and getting a call from management or the board: how can we prevent incidents like the one at our competitor or stakeholder? Silence follows. Because right now, you do not dare give the only correct answer. Namely: you do not have an adequate SOC SIEM solution because your security stack is incomplete.
In this article, you will find an underestimated line of thinking for answering that question properly.
A CISO's job description
As CISO, you have the worthy task of maintaining cyber resilience. A worthy task, but a devilishly difficult one too. You are the hub of the organisation: the point of contact for managers and directors, as well as colleagues and employees. It is no surprise that memes circulate about CISOs who are simply “done” after three years, mentally and physically. It is a job with plenty of stress, problems and challenges.
The security stack problem
It is therefore important for a CISO to know what the security stack needs. The problem? A security stack that is under- or overprotected. We see the latter increasingly often as many companies choose a SOC SIEM solution. “There, all sorted. One less difficult choice for our CISO.” Well… 😉
Why a 24/7 SOC is often not a good choice at all
SOCs are impressive. They have a great reputation, and fairly so, because they provide proactive alerts about malicious system and network activity. Perfect, and exactly what you want. That is not even all. A SOC SIEM solution also provides data collection and correlation in one place, plus compliance management and reporting. Impressive, right?
But what many large security suppliers do NOT consider when selecting the security stack is that a SOC is an oil tanker for many organisations when a speedboat would fit much better.
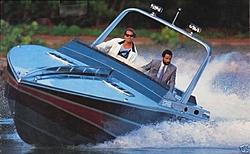
Large companies almost automatically choose the oil tanker. There is so much choice in cybersecurity. And what do you really need to protect against? So they choose the all-inclusive, hyper-secured 24/7 option. A Security Operations Centre (SOC) can be a good choice here, but is not always necessary for every organisation
We see nothing wrong with a solid oil tanker, unless you also choose one as a smaller business or with a small IT and security team. You are then overprotected and spend unnecessarily on a service you rarely or never need. For smaller businesses, the speedboat is therefore the smarter choice: fast, targeted, specific and with direct communication.
Most businesses often have no real need for a SOC, because:
- It is time-consuming: the enquiry, quotation process, customisation, learning curve and eventually implementation itself.
- It is complex: every organisation is different, as is every SOC and its implementation.
- It also brings sky-high costs.
The challenges of the right security stack
You do not have an adequate SOC SIEM solution, but want to do everything possible to give management or the board the right answer.
Several improvements to cyber resilience are rapidly brought forward to reduce the attack surface. The result? Choice overload. How do we avoid making the wrong choice? You do not want to invest in the first cybersecurity solution that comes along.
Preventing an incident is almost impossible. Before taking on even more enormous costs, get these two things right first:
- You want to know what is happening within your network at any time of day.
- You want to stay on top of every threat and be able to deal with it immediately.
The solution: a SOC delivering results within two days
What many businesses do not realise is that a solution exists that addresses all these challenges without compromising security, provided they are willing to look at their security stack in a specific, specialist way.
For businesses that want direct communication, quick action and no unnecessary costs, the speedboat, there is a solution they can have running within two days at a fraction of the cost of a SOC.
A system that could later integrate seamlessly with a potential oil-tanker SOC and even shorten the implementation time of a future SOC, because much of the logging is already available at a central point that can easily be connected to the new SOC.
What is that solution? Rapid7's InsightIDR. The strength of this measure is that data from various existing sources is analysed and used to detect risks and unusual behaviour.
For example, malicious exploitation of a major flaw such as Log4j (2021) was quickly detected by Rapid7.
This allows an organisation to add an extra analysis layer over its existing firewall and antivirus, sources such as Active Directory, LDAP and DHCP, and its PCs, laptops and servers, without creating a major additional administration burden. A particularly good, fast security measure for many businesses.
Businesses often look at their cyber resilience in the wrong way
For a hacker, only one thing matters: how quickly can I reach your pot of gold? That could be customer data, personnel files and sensitive information, or complete control of the network. That is why we like to look at our customers' cyber resilience as a hacker would, independently of trends, quick fixes and assumptions.
Is there panic in your business's security stack?
We are SECWATCH. We are the penetration testing specialists of the Netherlands and are happy to think things through with you by stepping into a hacker's shoes. From that perspective, we critically examine what you should and should not protect.
Put that nagging feeling of insecurity to rest and request a free Clarity Call here.